Security

What is TCP 3 Way Handshake

Fadıl

TCP or TCP/IP is the most used protocol on the internet. It is not only most used but also most secure. I have already explained to you what is TCP and how it works? In this article let’s discuss TCP 3 way handshake. It is also called 3 handshakes, TCP handshake but a handshake is common everywhere.

Must Read:Networking Protocols With Nmap

What is a 3-way handshake?

When any computer or net-enabled device tries to connect to any server or device to the port running on TCP then the connection will be established after three steps and so it is called TCP 3 way handshake.
Morris Worm Source Code and History

Morris Worm Source Code and History

Fadıl

Morris worm was created by a student from Cornell University named Robert Tappan Morris. It was created on November 2, 1988.

According to creator this worm was not created to damage but to find out the size of the internet. It worked by exploiting the vulnerabilities in Unix Sendmail, finger and many more. Later it was discovered that it has the power to crash the computer.

The link below shows how the Morris Worm is structured and where you can download code.

I LOVE YOU Virus Source Code and History

I LOVE YOU Virus Source Code and History

Fadıl

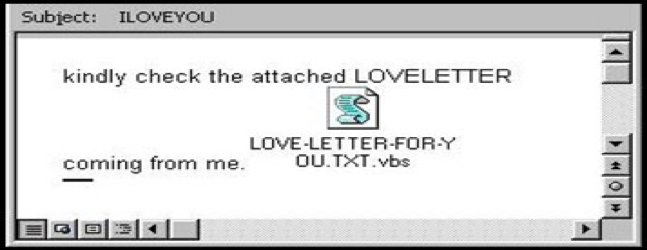
This post is about one of the greatest hacks all the time, ILOVEYOU virus aka love letter virus which affected 10 million computers and almost 10% percent of computers at the time of 2000.

Cheap History

On 5th May 2000, Reonel Ramones and Onel de Guzmen of Philippines created a virus name ILOVEYOU. It originated in Pandacan then spread across honking, Europe and then to US. This effected the loss around $20 billion.

Four Types of Nmap Scans Every Beginner Should Know (Part-1)

Four Types of Nmap Scans Every Beginner Should Know (Part-1)

Fadıl

“Every expert is once a beginner”

Nmap is undoubtedly the best scanning tool ever but only if you know how to use it. I have already shared you performing a simple nmap scan on any device. Here I am going to share the best beginner scans and first scans a pen-tester will do when he is pen-testing any network.

In this article, I will say you how these nmap scans will work when they are trying to access available, unavailable, filtered ports.

Four Types of Nmap Scans Every Beginner Should Know (Part-2)

Fadıl

This is the second part of Four types of nmap scans every beginner should know and you can read the first part here. I have discussed TCP and TCP connect scan there in that post and if you didn’t read it then first go and read it

Ping Scan(-sP)

Ping scan is a normal scan that you can perform without using nmap i.e.. with your default terminal in Linux or Unix based systems and from cmd in Microsoft Windows systems.